Offensive Security / Cybersecurity Education
Secure the system. Master the attack.
Expert penetration testing for modern organizations. Live, hands-on cybersecurity training led by offensive security professionals.
Two worlds, one mission
We secure what matters.
We train those who defend it.
The same offensive expertise powers both divisions: client engagements keep the teaching real, and teaching keeps the testing rigorous.
[01] — FOR ORGANIZATIONS
Offensive Security
Manual penetration testing and security assessments for web and mobile applications, networks and IoT. We find what scanners miss, prove the impact safely, and show your engineers exactly how to fix it.
- Web & API
- Mobile
- Network
- IoT
- Assessments
[02] — FOR LEARNERS & TEAMS
KnockSec Academy
Live, instructor-led cybersecurity courses on Zoom. Small cohorts, guided hands-on labs in authorised environments, and direct access to an instructor who does this work professionally.
- Live on Zoom
- Hands-on labs
- Cohort-based
- Beginner → Advanced
Positioning
Offensive expertise. Defensive confidence.
Attackers don't read your architecture diagrams. They probe what is actually deployed, combine small weaknesses into real impact, and move quickly. The only reliable way to know how your systems hold up is to test them the same way — with authorisation, rigour and a clear path to remediation.
The same is true for people. Security professionals become effective by doing the work under guidance, not by watching it. That is why KnockSec pairs real-world testing with live, practical education.
- 01
Manual and methodical
Every engagement and every lesson follows a repeatable methodology. Tools support the work; experienced judgement drives it.
- 02
Evidence, not opinion
Findings are reproduced and their impact demonstrated safely. Students learn the same discipline: prove it, document it, explain it.
- 03
Practice that transfers
Training is built from real-world testing experience — so what you practise in the lab is what the work actually looks like.
Penetration testing services
Independent testing for the systems your business runs on.
Scoped engagements, manual testing and reports engineered for remediation — for product teams, IT leaders and organisations preparing for customer security reviews.
Web Application Penetration Testing
OWASP-aligned manual assessments of web applications and their APIs — authentication, authorisation, business logic and injection classes, validated by hand.
- OWASP Top 10
- Access control
- Business logic
- API security
- Session management
Mobile Application Penetration Testing
Security assessments of Android and iOS applications covering local storage, authentication, transport security, platform interaction and the backend APIs the app relies on.
- Android
- iOS
- Mobile APIs
Network & Infrastructure Penetration Testing
Internal and external infrastructure testing: exposed services, misconfigurations, segmentation and the paths an attacker could use to move from a foothold to critical assets.
- External exposure
- Internal testing
- Segmentation
IoT Security Testing
Security assessments of connected devices and their ecosystems: device interfaces, communication protocols, firmware where scoped, companion apps and cloud APIs.
- Device interfaces
- Protocol analysis
- Firmware review (scoped)
Security Assessments
Vulnerability assessments, security architecture reviews, targeted reviews of specific features and independent remediation validation.
- Vulnerability assessment
- Architecture review
- Targeted review
Security methodology
Authorised. Reproducible. Actionable.
Every engagement follows the same disciplined lifecycle, so results are consistent, evidence-backed and tied to business risk — ending with fixes, not just findings.
// rules_of_engagement
scope: written & signed
targets: explicitly listed
impactful_tests: approval_required
critical_findings: escalated_immediately
- 01
Scope
Define targets, objectives, environments and rules of engagement. Nothing is tested without written authorisation.
- 02
Discover
Map the attack surface — applications, APIs, hosts, roles and trust boundaries — to understand how the system really works.
- 03
Assess
Manual, methodology-driven testing for vulnerabilities and design weaknesses, supported but never replaced by tooling.
- 04
Validate
Every finding is reproduced and its impact demonstrated safely. No unverified scanner output in your report.
- 05
Report
Findings ranked by business risk with evidence, reproduction steps and an executive summary leadership can act on.
- 06
Remediate
A debrief with your engineers, practical fix guidance and — when scoped — retesting to confirm issues are closed.
KnockSec Academy
Stop watching tutorials. Start thinking like a security professional.
Live Zoom classes
Scheduled sessions taught in real time — not a library of videos.
Guided hands-on labs
Practise every technique in isolated, authorised lab environments.
Real instructor interaction
Ask questions, get unstuck and receive feedback on your work.
Structured progression
Courses and learning paths that build methodically from fundamentals.
# lab-network · isolated training range
student@lab:~$ nmap -sV 10.10.20.0/24
Discovering hosts in scope…
10.10.20.14 22/ssh 80/http
10.10.20.31 445/smb
student@lab:~$
LAB OBJECTIVES
✓ Enumerate in-scope hosts
○ Identify exposed services
○ Document evidence
QUESTION
“Why is the SMB service a better first target here?”
AUTHORISED LAB
Isolated · scoped · legal
Featured live courses
Learn it live. Prove it in the lab.
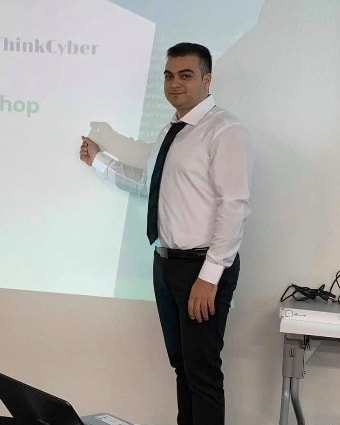
Every course is taught live on Zoom by Adonis Azzam, with guided practical labs in each module.
The course catalog is being finalised
New live cohorts will be announced here. Register your interest and we'll let you know when enrollment opens.
IN THE FIELD SINCE
2015
11+ years across testing, research & teaching
Meet your instructor
Adonis
Azzam
INFORMATION SECURITY CONSULTANT · OFFENSIVE SECURITY PROFESSIONAL · CYBERSECURITY INSTRUCTOR
Adonis Azzam brings years of practical experience in offensive security, cybersecurity research and hands-on professional education to every training session.
- OFFENSIVE LEADERSHIP
- Led an offensive services team delivering web, mobile, network & IoT testing
- RESEARCH & RESPONSE
- Malware analysis, digital forensics and incident response research
- TEACHING
- Professional courses, hands-on exercises and international workshops
- Web & mobile pentesting
- Infrastructure
- IoT security
- Digital forensics
- Malware analysis
- Incident response
- Python & Bash
The training experience
From first click to real capability.
- STEP 01
Choose a course
Pick the course or learning path that matches your level and goals.
- STEP 02
Reserve your place
Select a cohort, review the schedule and secure your seat.
- STEP 03
Join live Zoom lessons
Attend scheduled sessions and learn directly from the instructor.
- STEP 04
Practise in authorised labs
Apply every technique hands-on in isolated training environments.
- STEP 05
Receive feedback
Ask questions, review your approach and correct course in real time.
- STEP 06
Complete your training
Finish with practical skills and a methodology you can apply at work.
For engineering & security leaders
How secure is your next release?
Get an independent assessment before your customers, auditors or attackers do. You'll receive validated findings ranked by business risk and remediation guidance your engineers can act on immediately.